Ethical Hacking Course in Hyderabad
with Real Penetration Testing Labs
The ethical hacking course in Hyderabad at Cyber Security Academy is three months of instructor-led training in authorised offensive security — reconnaissance, scanning, enumeration, system hacking, web application testing and full penetration testing. Twenty modules, sixteen tools and four capstone projects, delivered as classroom batches in Kukatpally or live online.

Course snapshot
 Duration
3 months
 Mode
Classroom + live online
 Modules
20 modules, 16 tools
 Level
Beginner to advanced
 Next batch
2 November 2026
 Location
Kukatpally, Hyderabad
Ethical Hacking Course in Hyderabad — Quick Facts
Everything a prospective learner asks a counsellor in the first two minutes.
Course
Ethical Hacking Course in Hyderabad
Location
Kukatpally, Hyderabad
Training mode
Classroom + live online + recorded
Duration
3 months
Classroom fee
₹32,000
Online fee
₹25,000
Recorded course
₹9,999, lifetime access
Curriculum
20 modules, 16 tools, 4 capstone projects
Key areas
Recon, scanning, exploitation, web, wireless, cloud
Certification prep
eJPT, CEH, eCPPT and OSCP pathways
Next batch
2 November 2026
Prerequisites
None. Networking and Linux are taught from scratch.
Placement support and career outcomes
What we do, stated plainly, and what we do not claim.
Resume and portfolio review
Your CV is rebuilt around the penetration test reports you actually wrote, using the terms security recruiters screen for.
Mock interviews
Technical rounds on methodology, OWASP, privilege escalation and reporting, plus a scenario round on scoping an engagement.
Job-role selection
VAPT, web application testing and red teaming are different careers. We help you pick the one that fits how you work.
LinkedIn profile setup
Headline, skills, certifications and project section, so recruiter search surfaces you for testing roles.
Internship certificate
The classroom programme includes an internship certificate based on your completed capstone project work.
What we don't promise
No job guarantee, no guaranteed salary, no placement percentage. Any institute quoting those numbers cannot evidence them either.
Companies hiring ethical hacking professionals in Hyderabad
MNCs, global capability centres, consulting firms and specialist VAPT companies advertising testing roles in the Hyderabad market. We prepare you for their interview process. We are not claiming a hiring partnership with them.
Why choose this ethical hacking training in Hyderabad
Every reason below is something you can verify before you pay.
Our ethical hacking course in Hyderabad follows the sequence a real engagement follows — reconnaissance, scanning, enumeration, exploitation, escalation, then the report. You run sixteen tools in a lab you can reach 24/7, from the first scanning module onward.
Twenty modules cover the ground CEH examines, extended into wireless, mobile, IoT, OT and cloud. It finishes with four capstone projects, each producing a written security report — the deliverable that actually gets a tester hired.
Every technique is taught in scope, with authorisation, in a controlled lab. Module 1 covers the legal and ethical boundaries before you touch a tool.
Book a free demo class
See a real session before you commit — no obligation.
Authorisation taught first
Scope, rules of engagement and the legal boundary, before any tool. The difference between a tester and a defendant.
The full engagement sequence
Recon, scanning, enumeration, exploitation, escalation, reporting — in the order a real test runs.
16 tools with 24/7 lab access
Kali, Nmap, Burp Suite, Metasploit, SQLmap, Aircrack-ng and more, used rather than demonstrated.
Report writing is assessed
Every capstone produces a written report with findings, evidence and remediation. That is the real deliverable.
Networking and Linux from zero
Taught before any hacking tool, so non-technical learners are not lost in week three.
Web application depth
Three modules on web server, web application and SQL injection, tested in Burp Suite.
Wireless, mobile, IoT and OT
Four surfaces most syllabuses skip entirely, and where trained testers are scarce.
Cloud security included
Cloud identity, misconfiguration and configuration review — the fastest-growing source of findings.
Defences explained
IDS, firewalls and honeypots, so you understand what detects you and why.
Honest certification advice
eJPT before CEH for most freshers. We will tell you when a certification is not worth its price yet.
Classroom option in Kukatpally
In-person batches at our Nizampet X Roads centre, plus live online for everyone else.
EMI and instalment options
Classroom and online fees can be paid in EMI or two instalments.

Ethical Hacking Course Syllabus — 20 Modules
Twenty modules that follow the sequence of a real penetration test — the topics, the lab and the outcome for each one.
Introduction to Ethical Hacking
Scope, authorisation and the law. What separates a penetration test from a crime.
You will cover
✓ Hacking concepts
✓ Attack classes
✓ Scope and rules of engagement
✓ Legal and ethical practice
Outcome: you understand what authorisation actually means before you touch a tool.
Footprinting and Reconnaissance
Everything an attacker learns before sending a single packet.
You will cover
✓ Passive recon
✓ Active recon
✓ Domain and DNS intel
✓ OSINT sources
Lab: build a full OSINT profile of an authorised target.
Scanning Networks
Finding what is alive, what is listening and what it is running.
You will cover
✓ Network discovery
✓ Port scanning
✓ Service identification
✓ OS detection
Tools: Nmap, Netcat, banner grabbing.
Enumeration
Turning open ports into usable detail about users and services.
You will cover
✓ User enumeration
✓ Service enumeration
✓ Windows and Linux
✓ SMB, SNMP, LDAP
Outcome: the step most beginners skip and most interviews test.
Vulnerability Analysis
Finding weaknesses is easy. Ranking them correctly is the skill.
You will cover
✓ CVE and CVSS
✓ Scanning
✓ Risk prioritisation
✓ False positive triage
Tools: Nessus, OpenVAS, Nikto.
System Hacking
How accounts get taken over, and how privilege escalates.
You will cover
✓ Authentication weaknesses
✓ Password security
✓ Credential testing
✓ Privilege escalation
Tools: John the Ripper, Hashcat.
Malware Threats
What lands on the machine after the first foothold.
You will cover
✓ Viruses and worms
✓ Trojans
✓ Ransomware
✓ Rootkits
Outcome: you can describe an infection chain end to end.
Sniffing
Reading the traffic that was never meant for you.
You will cover
✓ Packet capture
✓ Traffic analysis
✓ Protocol analysis
✓ Detection of sniffing
Tools: Wireshark, tcpdump.
Social Engineering
The technique behind most successful breaches.
You will cover
✓ Phishing
✓ Pretexting
✓ Impersonation
✓ Awareness controls
Lab: analyse a real phishing chain and its indicators.
Denial of Service
Availability as an attack surface.
You will cover
✓ DoS and DDoS concepts
✓ Common methods
✓ Traffic analysis
✓ Detection and mitigation
Outcome: you can explain amplification and rate limiting.
Session Hijacking
Stealing access without ever stealing a password.
You will cover
✓ Session management
✓ Token security
✓ Hijacking techniques
✓ Countermeasures
Lab: session testing in an authorised web app.
IDS, Firewalls and Honeypots
The defences you will meet, and how testers work around them.
You will cover
✓ Firewall fundamentals
✓ IDS and IPS
✓ Honeypots
✓ Evasion concepts
Outcome: you can test defences, not just systems.
Web Server Security
The layer beneath the application.
You will cover
✓ Server fundamentals
✓ Common misconfigurations
✓ Hardening
✓ Server-side testing
Tools: Nikto, Gobuster.
Web Application Security
Where most real-world findings come from.
You will cover
✓ App architecture
✓ AuthN and AuthZ
✓ Access control
✓ Input validation
Lab: a full web application security assessment in Burp Suite.
SQL Injection
The single most-demonstrated vulnerability in interviews.
You will cover
✓ Injection fundamentals
✓ Testing methodology
✓ Database security
✓ Remediation
Tools: SQLmap, manual payload testing.
Wireless Network Security
Attacks that do not need a network cable.
You will cover
✓ Wi-Fi protocols
✓ Wireless threats
✓ Authentication attacks
✓ Wireless hardening
Tools: Aircrack-ng.
Mobile Platform Security
Android and iOS as an attack surface.
You will cover
✓ Mobile fundamentals
✓ Android security
✓ iOS security
✓ Mobile app testing
Outcome: you can assess an app, not just a website.
IoT and OT Security
Devices that were never designed to be attacked.
You will cover
✓ IoT architecture
✓ Common IoT flaws
✓ Device security
✓ OT and ICS basics
Outcome: a growing niche with very few trained testers.
Cloud Security
Where the workloads went, and the misconfigurations followed.
You will cover
✓ Cloud fundamentals
✓ Identity and access
✓ Cloud attack surface
✓ Configuration review
Lab: a cloud configuration security review.
Cryptography
How data stays private, and how implementations fail.
You will cover
✓ Symmetric and asymmetric
✓ Hashing
✓ Digital signatures
✓ PKI and certificates
Outcome: you can explain TLS and certificate validation clearly.
Ethical hacking tools you will use
Each tool, what it does, and where it shows up in the labs and projects.
Ethical hacking skills you will learn
Twelve concrete capabilities you walk out with, aligned to what security recruiters screen for.
Reconnaissance
Collecting intelligence on an authorised target before testing begins.
OSINT
Using publicly available information to map an attack surface.
Network scanning
Identifying live hosts, open ports, services and operating systems.
Enumeration
Extracting user, share and service detail from exposed systems.
Vulnerability assessment
Scanning, triaging and ranking findings by real risk.
Exploitation
Controlled, authorised exploitation with Metasploit and manual techniques.
Privilege escalation
Turning a low-privilege foothold into administrative access.
Web application testing
OWASP-aligned testing for injection, access control and auth flaws.
SQL injection
Manual and automated injection testing, and how to remediate it.
Wireless testing
Wi-Fi protocol weaknesses and authentication attacks.
Report writing
The deliverable that gets you paid: findings, evidence, remediation.
Defensive awareness
IDS, firewalls and honeypots, so you understand what detects you.
Ethical hacking capstone projects you will build
Four projects, run in an authorised lab. Each one ends in a written report you can show an employer.
Network security assessment
Web application security testing
Vulnerability assessment
End-to-end penetration test
Who can join this ethical hacking course?
Suitable for a wide range of learners. No prior security experience is required to start.
Freshers and students
Start from networking and Linux fundamentals. No prior security experience needed.
IT support engineers
Turn systems knowledge into an offensive security skill set.
Network engineers
You already understand the protocols. Learn how they are attacked.
System administrators
Windows, Linux and AD knowledge transfers directly into system hacking.
Testers and QA engineers
Testing instincts map almost one-to-one onto penetration testing.
Developers
Understand the attacks your code has to survive.
Career switchers
A structured path into VAPT and penetration testing roles.
Future penetration testers
Ready to move from curiosity about hacking into an authorised, paid testing role? This is your on-ramp.
Recon · Exploitation · VAPT · ReportingShould a fresher take CEH first?
Usually not. Here is the honest comparison, with the real 2026 prices.
Junior Penetration Tester

Certified Ethical Hacker
CEH is the certification most Hyderabad job descriptions name, so it is worth holding eventually. It is also roughly seven times the price of eJPT. Our advice is to build hands-on evidence first, sit eJPT, then take CEH when you have experience behind it or an employer willing to fund it. We prepare you for both.
Certification path we prepare you for
What you receive on completion
On completing the programme you receive a Cyber Security Academy course completion certificate — a record of the modules you finished and the penetration test reports you produced. It is separate from any vendor certification, which is issued by the certifying body.
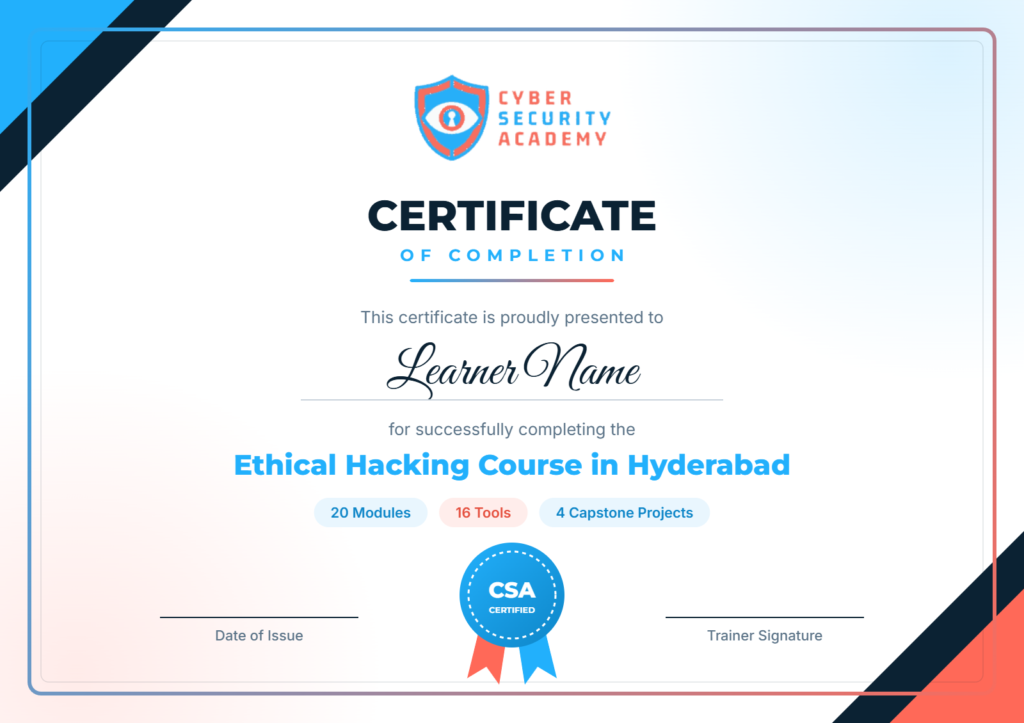 Sample · course completion certificate
Your trainer
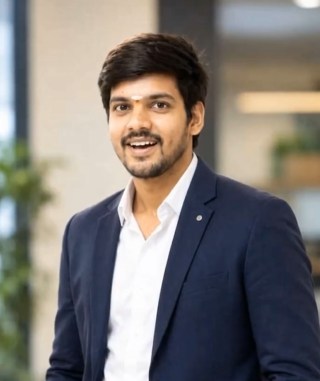 Lead Trainer
Mr. Praveen K
Lead trainer, ethical hacking and penetration testing.
10+ years of industry experience, teaching reconnaissance, exploitation, web application testing and report writing from the perspective of someone who has run real engagements rather than only studied them.
Specialisations
Penetration testing, web and network VAPT, vulnerability assessment, wireless and cloud testing.
Teaching approach
Every concept lands in a lab the same session. No module ends without something run against a target.
Mentorship
1:1 career mentorship and guidance on which certification path fits your background and budget.
Support
Doubt-clearing sessions, technical support and WhatsApp learning support between classes.
Learning modes and upcoming batches
Three ways to take the same 20-module syllabus.
Recorded course
Lifetime access ₹9,999✓ Fundamentals to advanced modules
✓ 1 capstone project included
✓ Tools walkthrough and certification guidance
✓ WhatsApp learning support
Classroom
Starts 2 November 2026 ₹32,000✓ 3 months, instructor-led practical training
✓ 4 capstone projects, 16 tools
✓ 24/7 lab access
✓ Internship certificate and placement assistance
Live online
Weekday and weekend ₹25,000✓ Live interactive classes, same trainer
✓ Daily recordings and LMS access
✓ Hands-on labs and real projects
✓ Placement assistance and mock interviews
EMI and two-instalment payment options are available on classroom and online training.
Check us out before you enrol
We would rather you verify everything than take our word for it. Here is exactly how.
Sit in on a live class
Book a free demo and watch an actual session — the trainer, the pace, the lab setup and the batch you would join. Nothing is staged for visitors.
Read our Google reviews
Open our Google Business Profile and read what learners wrote there. Google reviews are tied to real accounts, which is why we point you to them rather than printing quotes here.
Read reviews on GoogleAsk to see a real report
Ask what a finished penetration test report looks like. In this field the report is the product. If an institute cannot show you one, the projects are a line on a brochure.
Ask about lab access
Ask how many hours a day you can reach the lab and on whose infrastructure. Hands-on time is the difference between a certificate and a skill.
Ask about authorisation
Ask how they teach scope and legal boundaries. Any course that skips this is teaching you to get into trouble.
Compare the syllabus
Our full 20-module syllabus is on this page. Compare it module by module — particularly on wireless, IoT, OT and cloud, which most syllabuses skip.
Ethical hacking salary in Hyderabad and India
Indicative market ranges by city. These are estimates, not offers.
Indicative annual range. Very high demand.
Indicative annual range. Very high demand.
Indicative annual range. High demand.
Indicative annual range. Very high demand.
Indicative annual range. High demand.
Indicative annual range. Junior pentest roles.
Disclaimer. Salary figures shown are indicative market estimates and are not a guarantee of earnings. Actual compensation depends on experience, skills, certifications, employer and interview performance.
Career opportunities after the ethical hacking course
The roles this syllabus maps to, and what each one is actually accountable for.
Ethical Hacker
Authorised testing of systems and applications. Key skills: recon, exploitation, reporting.
Penetration Tester
Full-scope engagements against networks and applications. Key skills: methodology, Metasploit, documentation.
Junior Penetration Tester
Entry-level testing under supervision. Key skills: scanning, enumeration, guided exploitation.
VAPT Analyst
Vulnerability assessment and penetration testing delivery. Key skills: Nessus, Burp Suite, CVSS.
Vulnerability Analyst
Scanning, triage and remediation tracking. Key skills: CVE, CVSS, prioritisation.
Web Application Security Tester
Application-layer testing against OWASP categories. Key skills: Burp Suite, injection, access control.
Network Security Analyst
Defending the network layer. Key skills: firewalls, traffic analysis, segmentation.
Security Consultant
Client-facing assessment and advisory. Key skills: breadth, communication, reporting.
Red Team Operator
Adversary simulation against mature defences. Key skills: evasion, tradecraft, OPSEC.
Security Analyst
Broad defensive and offensive work in smaller teams. Key skills: detection plus testing.
Bug Bounty Hunter
Independent testing on public programmes. Key skills: web testing, persistence, reporting.
Cyber Security Consultant
Advisory across testing, risk and compliance. Key skills: assessment plus GRC literacy.
Ethical hacking roadmap: beginner to advanced
The order matters. Starting on exploitation tools before networking is the most common reason learners stall.
Foundations
The groundwork every technique depends on. Taught before any hacking tool.
• Security fundamentals
• Networking
• Linux and Windows
Information gathering
Everything an attacker learns before touching the target.
• Footprinting
• Reconnaissance and OSINT
• Scanning and enumeration
Exploitation
Turning a finding into proven access, under authorisation.
• Vulnerability analysis
• System hacking
• Privilege escalation
Application and network surfaces
Where most real findings come from in a paid engagement.
• Web and SQL injection
• Wireless and mobile
• IoT, OT and cloud
Job ready
Reports, certification and the interview work that turns skills into an offer.
• 4 capstone reports
• eJPT and CEH prep
• Mock interviews
How this differs from other ethical hacking institutes in Hyderabad
Category-level comparison. We do not name competitors, and every row is something you can check before enrolling.
Why ethical hacking is a strong career in Hyderabad in 2026
Three things specific to this city and this year.
Hyderabad is a GCC city
The global capability centres in Hitech City, Gachibowli and Madhapur run security testing for parent companies abroad. VAPT and application security work is delivered from here continuously.
The consulting firms hire testers
Deloitte, EY, PwC and KPMG all run security testing practices in Hyderabad. Consulting is the most common first employer for a certified tester in this market.
Evidence beats credentials
Testing roles hire on demonstrated ability — a written report, a lab result, a bug bounty finding. A portfolio counts more here than in almost any other IT field.
Common questions, answered directly
Is ethical hacking a good career in 2026? Yes, if you can test methodically and write up what you found. The demand is for people who produce reports, not people who run scanners.
Can a fresher get in? Yes. Junior penetration tester and VAPT analyst roles hire from outside computer science regularly, on the strength of practical evidence.
How do I start? Networking and Linux, then reconnaissance and scanning, then exploitation, then web and wireless, then projects and certification. In that order.
Frequently asked questions
The twenty questions counsellors are asked most often, answered plainly.
What is the ethical hacking course in Hyderabad?
It is instructor-led training in authorised offensive security — reconnaissance, scanning, enumeration, exploitation, web application testing and penetration testing. Cyber Security Academy delivers it as classroom training in Kukatpally and as live online batches across 20 modules over three months.
What is the duration of the ethical hacking course?
Three months. Classroom and live online batches follow the same 20-module syllabus, with weekday and weekend options so you can fit it around work.
What is the ethical hacking course fee in Hyderabad?
Classroom training is ₹32,000 and live online training is ₹25,000, with a recorded course at ₹9,999. EMI and two-instalment options are available. Certification exam fees are paid separately to the certifying body.
Do I need a technical background?
No. The course starts with networking and Linux fundamentals before any hacking tool. IT support engineers, testers, developers and complete beginners start from the same point.
Is ethical hacking legal?
Yes, when it is authorised. Every technique on this course is taught within a defined scope, with written permission from the system owner, in a controlled lab. Module 1 covers scope, rules of engagement and the legal boundaries in detail.
Is this course CEH aligned?
The syllabus follows the domain structure CEH examines — reconnaissance, scanning, enumeration, system hacking, web and wireless security, cloud and cryptography. We prepare you for the exam. EC-Council issues the certification, not us.
Should a fresher take CEH first?
Usually not. CEH costs around $1,699. eJPT at roughly $250 is the more realistic first credential for a fresher, and it is hands-on. CEH and OSCP make more sense once you have practical experience and, ideally, an employer contributing.
How many tools will I use?
Sixteen, with 24/7 lab access: Kali Linux, Nmap, Wireshark, Burp Suite, Metasploit, Recon-ng, Nessus, OpenVAS, Nikto, Gobuster, John the Ripper, Hashcat, Aircrack-ng, SQLmap, OWASP ZAP and Netcat.
Are real projects included?
Yes, four capstone projects: a network security assessment, a web application security test, a vulnerability assessment and a full end-to-end penetration test with a written report.
Is report writing covered?
Yes, and it matters more than most learners expect. The deliverable in a real engagement is the report — findings, evidence, risk rating and remediation. Every capstone project produces one.
Is web application security covered in depth?
Yes, across modules 13 to 15: web server security, web application architecture and access control, and SQL injection as its own module, tested in Burp Suite and SQLmap.
Is wireless hacking included?
Yes, as module 16. Wi-Fi protocols, wireless threats and authentication attacks, practised with Aircrack-ng in the lab.
Do you cover cloud and IoT?
Yes. Module 18 covers IoT and OT security and module 19 covers cloud security, including identity, misconfiguration and configuration review — two areas with far more demand than trained testers.
What job roles can I apply for?
Ethical Hacker, Junior Penetration Tester, VAPT Analyst, Vulnerability Analyst, Web Application Security Tester and Security Consultant are the common entry points in the Hyderabad market.
What salary can I expect in Hyderabad?
Ethical hacking roles in Hyderabad commonly advertise around ₹5.5–9 LPA, with Bengaluru at ₹6.5–11 LPA. Entry-level roles typically start lower, around ₹4–7 LPA. These are indicative market ranges, not a guarantee.
Is the training available online?
Yes. Live online batches run the same syllabus with the same trainer, with daily recorded sessions for revision and LMS access.
Is classroom training available in Hyderabad?
Yes, at Dr Atmaram Estates, Nizampet X Roads, near JNTU. Learners travel from KPHB, JNTU, Ameerpet, Madhapur, Hitech City and Gachibowli.
Is placement assistance provided?
Yes: resume building, LinkedIn profile improvement, technical interview preparation, mock interviews and job applications. We do not guarantee placement.
Can I attend a demo before paying?
Yes. Book a free demo class and sit in on a real session — the trainer, the pace, the labs and the batch you would actually join.
Is there a job guarantee?
No. We do not guarantee placement or any salary outcome. What we provide is job-oriented training, a project portfolio, interview preparation and placement assistance. The hiring decision belongs to the employer.
Ready to start your
ethical hacking career?
Sit in on a live session before you commit. You will see the curriculum, the trainer, the lab setup, the batch timings and how the projects work.
No obligation. Speak with a course counsellor and find out whether this programme is right for you.
Other courses at Cyber Security Academy
Visit or contact us
Our centre is at Dr Atmaram Estates, Nizampet X Roads, close to KPHB and JNTU.
 Find us on Google Maps
Dr Atmaram Estates, Nizampet X Roads
Open map →